Standards & safety
EU Authorities Urge Immediate Action After Cyberattacks on Commercial Refrigeration Systems
The European Commission and ENISA have called on businesses to take immediate cybersecurity steps after confirmed attacks on commercial refrigeration systems in several EU member states. The incidents coincide with new obligations under the Cyber Resilience Act and NIS2 Directive, which impose reporting and design-security requirements on manufacturers.
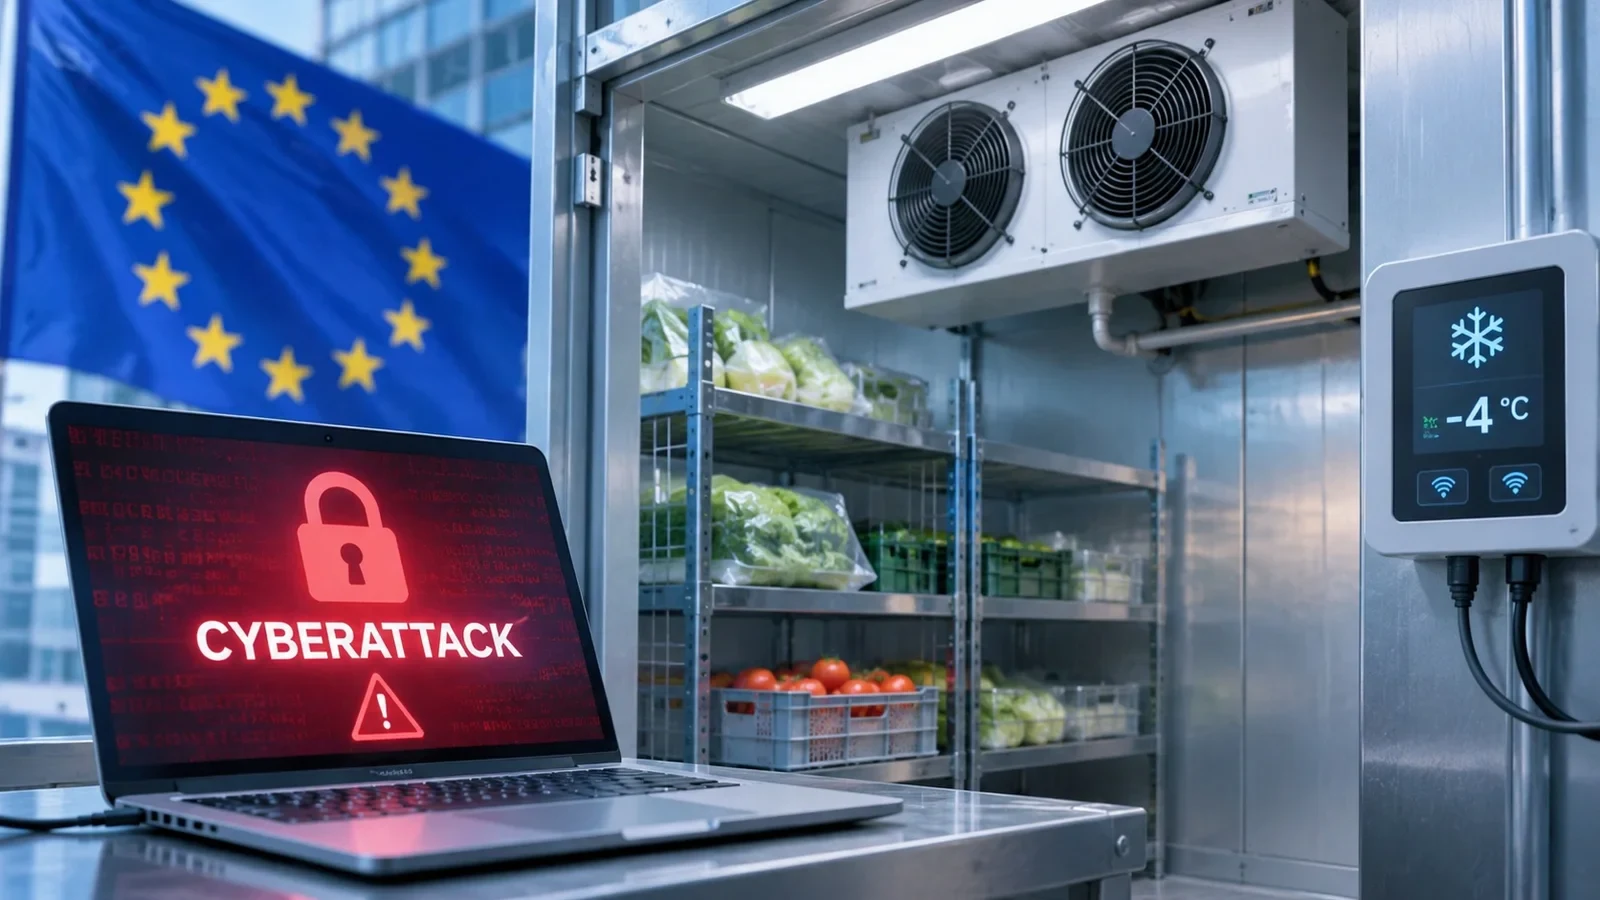
The European Commission and the European Union Agency for Cybersecurity (ENISA) have called on businesses to take immediate cybersecurity measures after confirmed attacks on commercial refrigeration systems in multiple EU member states. A joint statement issued on November 4, 2026, confirmed incidents affecting refrigeration systems and similar connected devices since October 11, followed by a second wave on November 1–2.
Coordinated response across EU bodies
The Commission and ENISA are coordinating with national authorities to monitor the incidents, exchange information and assess the situation. The response involves the Commission's Directorate-General for Communications Networks, Content and Technology (DG CNECT), Europol's European Cybercrime Centre (EC3), the EU Computer Security Incident Response Teams Network, and the European Cyber Crisis Liaison Organisation Network (EU-CyCLONe). Affected member states are investigating the incidents and providing guidance to businesses, while national cybersecurity response teams and EU coordination bodies continue exchanging information.
Regulatory backdrop: Cyber Resilience Act and NIS2
The incidents unfold against the implementation of EU cybersecurity legislation. Under the Cyber Resilience Act, manufacturers of hardware and software products have been required since September 11, 2026, to report severe security incidents and actively exploited vulnerabilities through the EU's Single Reporting Platform. Additional requirements taking effect on December 11, 2027, will oblige manufacturers of products with digital elements to integrate security into product design, provide cybersecurity support throughout the product lifecycle, and address vulnerabilities without delay.
Organisations covered by the NIS2 Directive must implement appropriate cybersecurity risk management measures and report significant incidents to relevant national authorities.
What operators should do
Organisations operating potentially vulnerable refrigeration equipment have been advised to take immediate steps to reduce their exposure to cyber threats. ENISA and other EU cybersecurity bodies will continue monitoring developments and coordinating information-sharing as investigations proceed.
Source: refindustry.com.
ORIGINAL SOURCE
Refindustry ↗Visit the original source for additional details.